SSO with SAML
Coralogix supports SAML 2.0 single sign-on (SSO), so you can let users sign in with your identity provider (IdP) and manage access centrally. You configure SAML on the SAML Configuration page, at Settings, then Account, then Configure SAML.
This page covers how SAML SSO works, how to create and manage configurations, organization-level SAML, and provider-specific setup for common IdPs.
If you plan to pair SAML with SCIM, add users through SCIM and delete any existing users before starting the SCIM integration (you can leave one admin user). After the SCIM integration is complete, recreate all users through SCIM.
How SAML SSO works
A SAML configuration represents one IdP integration. You can create more than one configuration for the same team, and each active configuration becomes an SSO option that users can choose at sign-in.
Each configuration:
- Represents one IdP integration, with its own metadata and settings.
- Can be Active or Inactive. Only active configurations appear as SSO options at sign-in.
- Can be team-level, or inherited from an organization-level configuration.
Multiple configurations can be active at the same time. When more than one is active, users choose their provider at sign-in; when only one is active, they can be redirected straight to it.
This supports enterprises with multiple identity domains, managed service providers accessing several customer environments, and staged migrations between IdPs, since you can validate a new provider before you activate it.
Create a SAML configuration
Create configurations from the SAML Configuration page. Select Add SAML configuration to open the Create SAML Provider wizard:
- Provider details. Enter a Display name users recognize at sign-in (for example, Okta - Production) and an optional Description. If your team belongs to an organization, choose the configuration level (team or organization).
- Coralogix service provider details. Copy the Coralogix service provider values (metadata URL, ACS URL, entity ID, binding, and relay state) into your IdP.
- Identity provider metadata. Upload your IdP's
metadata.xmlfile by dragging it in or selecting Upload XML. - Default groups. Select the default groups assigned to users the first time they sign in.
Save the configuration, then activate it when you're ready. For provider-specific steps, see Provider-specific setup.
Advanced settings
After a configuration is created, open it from the SAML Configuration page and expand Advanced settings to enable optional behaviors.
Advanced settings are read-only for legacy SAML configurations, and for anyone without permission to manage SAML configurations. The toggles are visible but cannot be changed.
Enable IdP-initiated login
Allow users to start sign-in directly from their IdP application tile (for example, Okta or Microsoft Entra ID). When disabled, users must start authentication from the Coralogix sign-in page, which prevents unsolicited SAML assertions.
Skip email verification for verified organization domains
Skip the email confirmation step for users provisioned through this configuration whose email domain your organization has already verified.
- Prerequisite: an organization admin must verify the domain first, in Domain manager.
- Unverified domains: users whose email domain is not verified continue through the standard email verification flow.
- Teams outside an organization: the domain check resolves the team's parent organization, so a team that does not belong to one never qualifies for the skip.
Assign default groups on every SSO login
By default, a configuration's default groups are assigned only on the login that creates or reactivates a user's membership in a team, so members who already exist do not receive default groups you add later. Enable this setting to apply the default groups on every SSO login.
- Additive only: memberships are only added, never removed. Groups assigned by an admin or mapped from your identity provider stay in place.
- Default: off, configured per SAML configuration.
- Organization-level configurations: each assigned team's own default groups apply independently.
- Legacy configurations: not supported.
Set a configuration as the default for a domain
Set a configuration as the default for one or more of the organization's verified domains. Once set, Coralogix offers this configuration's SSO directly to anyone who signs in with an email in that domain, with no team-selection step. See Sign in with an email domain.
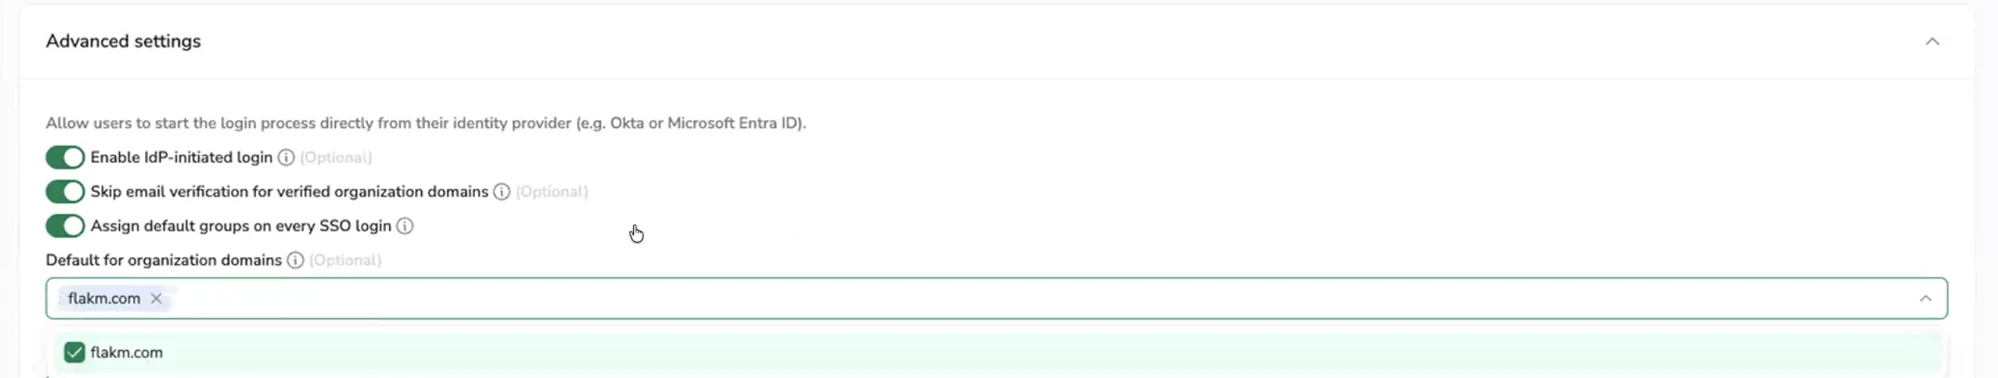
Select Default for organization domains and select from your organization's verified domains.
- Prerequisite: an organization admin must verify the domain first, in Domain manager. If your organization has no verified domains, this field does not appear.
- One owner per domain: a domain can be the default for only one configuration, team-scoped or org-scoped, at a time. A domain another configuration already owns appears disabled and shows which configuration owns it. Remove the domain from its current configuration before adding it to another.
- Teams outside an organization: a team that does not belong to an organization has no domains to choose, so this field does not appear for it.
- Active configurations only: an inactive configuration is skipped at sign-in, even if it still owns a domain.
- Automatic release: Coralogix removes a domain from a configuration if the domain's verification is revoked, the owning team leaves its organization, the organization is deleted, or the configuration is deactivated or deleted. The sign-in shortcut for that domain stops appearing as soon as the domain is released.
The SAML Configuration list shows which domains each configuration owns.
Sync groups from your identity provider
Have your identity provider (IdP) drive a user's Coralogix group memberships on every SSO login, instead of managing them by hand in Coralogix. Choose one of three modes:
-
Off: group memberships are managed in Coralogix only.
-
Use existing groups: adds users to groups whose name matches a value sent by the IdP. Values with no matching group are ignored.
-
Create missing groups: does the same, and also creates a group for each value with no match. A created group has no role until you assign one.
-
Default: off, configured per SAML configuration.
-
Legacy configurations: not supported.
For how matching, removal, and organization-level team qualification work, see SAML group sync.
Default groups
Default groups determine the initial roles assigned to users when they are first provisioned in a team. They apply only on the login that creates or reactivates the membership: if a user was already provisioned another way (for example, through SCIM) and then signs in through SSO for the first time, the default groups are not applied. To apply them on every SSO login, enable Assign default groups on every SSO login.
For more information, see Groups.
Manage SAML configurations
From the SAML Configuration page you can add, edit, activate or deactivate, delete, and test configurations. The list shows each configuration's status (Active or Inactive), its last-modified and last-activated timestamps, and whether it has never been activated.
- Activate makes a configuration available as an SSO option at sign-in. Multiple configurations can be active at once.
- Deactivate removes it from the available SSO options. Users cannot sign in with an inactive configuration.
- Delete permanently removes a configuration. Deactivate an active configuration before you delete it.
- Test runs a real sign-in through the IdP, so you can validate a configuration before activating it.
Sign-in experience
Coralogix supports both SP-initiated and IdP-initiated sign-in.
Start sign-in from Coralogix
- Go to the Coralogix sign-in page.
- Select your team, if prompted.
- Select Log in with SSO.
- If more than one SSO provider is active, select your provider.
- Complete authentication in your IdP.
If only one provider is active, you may be redirected to it directly. If you already have an active session with your IdP, Coralogix signs you in without prompting for credentials again.
Sign in with an email domain
This feature is available for early-access customers. To request access and confirm your organization meets the feature criteria, contact your account representative or Support.
If your email domain is set as the default for a configuration, Coralogix offers that configuration's SSO as soon as you enter your email, with no team name required.
- Go to the Coralogix sign-in page without specifying a team.
- Enter your email.
- Select Log in with
<domain>SSO, where<domain>is your email's domain (for example, Log in with acme.com SSO). Complete authentication with your identity provider.
You land in the configuration's team: the team itself for a team-scoped configuration, or the organization's default team for an org-scoped one. If you already have an active session with your IdP, sign-in completes without prompting for credentials again.
You can also:
- Use password: sign in with your password instead of SSO.
- Log in with other SSO: continue to the standard team-selection step, for example to sign in to a configuration in another organization.
A failed or slow domain lookup never blocks password sign-in: if Coralogix can't resolve your domain, you see the standard sign-in flow.
IdP-initiated sign-in
When IdP-initiated login is enabled for a configuration, users can start sign-in from their IdP application tile. Coralogix validates that the IdP is configured and authorized for the selected team, and grants access only if the configuration is active and valid.
You can add multi-factor authentication for extra protection.
Organization-level SAML
Organization-level SAML lets you configure an IdP once and assign it to multiple teams, which reduces duplicate configuration and keeps authentication policies consistent. Organization-level configurations coexist with team-level ones: a team's available SSO options are the combination of the organization configurations assigned to it and any team configurations created for it.
Before you begin
To create or manage organization-level SAML, you must be an organization admin. Team admins can view the organization configurations assigned to their team and edit the default groups for their own team, but cannot create, edit, activate, or delete them.
Create an organization-level configuration
- Go to Settings, then Account, then Configure SAML and open the Organization configurations section.
- Select Add SAML configuration.
- Set Configuration level to Organization. This cannot be changed after the configuration is created.
- Configure your identity provider: configuration name, optional description, identity provider metadata, and Coralogix service provider details.
- Under Default groups per team, choose which teams the configuration applies to:
- Turn on Apply to all teams to cover every team in the organization, including teams added later.
- Leave it off and select the teams under Teams this configuration applies to.
- (Optional) Set default groups for each assigned team.
- Save the configuration, then activate it when ready.
Assign configurations to teams
Assign each organization-level configuration to one or more teams, or apply it to all teams (teams added later are included automatically). Only assigned teams expose the configuration at sign-in. Removing a team makes the configuration unavailable for sign-in to that team; existing users and their permissions remain in place.
Provisioning
Organization-level SAML supports Just-in-Time (JIT) provisioning. On a user's first successful sign-in, user accounts are created as needed, team memberships are provisioned for the assigned teams, and default groups are applied to newly provisioned users where configured. Existing users keep their current permissions.
Permissions
| Action | Organization admin | Team admin |
|---|---|---|
| View organization-level SAML | ✅ | ✅ (assigned teams only) |
| Create organization-level SAML | ✅ | ❌ |
| Edit organization-level SAML | ✅ | ❌ |
| Delete organization-level SAML | ✅ | ❌ |
| Activate or deactivate organization-level SAML | ✅ | ❌ |
| Assign teams | ✅ | ❌ |
| Configure default groups | ✅ | ✅ (their team only) |
| Create, edit, or delete team-level SAML | ✅ | ✅ |
Provider-specific setup
The following walkthroughs cover setup for common identity providers. If you have questions, contact us via the chat bubble in the web app.
Integrate with Google as a SAML IdP
View dedicated Google instructions here.
Integrate with OneLogin as a SAML IdP (EU1 regional users)
These instructions apply only to EU1 region-based users. Integration instructions for all other regions can be found in the following section.
Navigate to your administration panel and navigate to applications. Click on Add App button and choose Coralogix.

Choose a name to display (default is Coralogix), add a description if you'd like, and Save.

Coralogix also supports IdP-initiated flow enabling direct connection to Coralogix from your Onelogin App portal. To enable, once our connector is saved, go to Configuration and insert your Coralogix account company ID (in your Coralogix account, go to Settings, then Send your data) into the RelayState dialog box. Click Save.

Download the SAML Metadata XML file.

Upload the metadata file to our web app via Settings, then Configure SAML.

Integrate with OneLogin as a SAML IdP (Non-EU1 regional users)
Navigate to Applications and select Add App.

Search for and select SAML Test Connector (IdP).

Go to Configuration and add the details according to the following example. This particular example is for an EU2-based team.

Click Save. The newly prepared XML configuration may be uploaded to the relevant Coralogix team.
Integrate with Okta as a SAML IdP
We strongly recommend setting up your Okta SSO using SCIM rather than SAML.
Create a new SAML 2.0 app integration. In Okta, navigate to Applications, then Create App Integration, then SAML 2.0. Click Next.

In General Settings, enter the App name used by Okta to display the application name to users (e.g., "Coralogix Production").

In Coralogix, navigate to Settings, then Configure SAML.

- Single sign-on URL > Assertion Consumer Service URL
- Audience URI (SP Entity ID) > Service Provider Entity ID/Audience
- Default RelayState >
<Company ID or Name of your Coralogix team> - Name ID Format should be set to EmailAddress
Once complete, click Next and complete the last stage. Click Finish.
Scroll down to SAML Signing Certificate, click on the Actions drop-down menu and select "View IdP metadata". Copy the metadata into a text file and save it as .xml.

Returning to the Coralogix SAML configuration, you must upload the file you just created by selecting Choose file and selecting XML file you saved in the previous step.
After the upload completes, refresh the page. Coralogix regenerates the SAML endpoints and appends a ?tid=<value> parameter to the URLs.

Coralogix regenerates the SAML URLs after the first metadata upload. You must update the Okta application with the new URLs containing the ?tid=<value> parameter.
Copy the updated Assertion Consumer Service URL and Service Provider Entity ID values from Coralogix.
Each URL now includes a ?tid=<value> parameter.
You must update the Okta application with these regenerated URLs-including the ?tid=<value> parameters-to complete the SAML setup.
In Okta, open your Coralogix SAML app and replace the corresponding fields with the updated URLs. Save the application.
Because the Okta metadata file you downloaded earlier did not include the tenant-specific URLs, you must regenerate it.
In Okta, open the SAML Signing Certificate section and select View IdP metadata. Download the updated metadata file.
Return to the Coralogix SAML configuration page and upload this new file. This final upload completes the SAML configuration.
Integrate with Azure as a SAML IdP
Enter https://portal.azure.com/.
After logging into Azure, go to Azure Active Directory tab.
Select Enterprise applications service.
Choose 'New application'.
Choose 'Non-gallery application'.
Name it (for example, CoralogixSSO) and click Add.
Go to Configure single sign-on.
Select SAML-based Sign-on as the SSO mode.

Next, you will need to add Coralogix service provider details to the configuration in Azure as follows:
From Coralogix web app, go to Settings, then Configure SAML. Configure the following:
* Service Provider Entity ID/Audience
* Assertion Consumer Service URL
In the Azure portal (example paths):

If you would like to log in to a specific Coralogix team or account from your Azure SSO app directly, add the Coralogix team name to the Relay State option, as part of your basic SSO configuration.

Choose 'user.mail' as the value for User Identifier.

At the bottom of the page in step 5, click Configure CoralogixSSO.
Scroll down to step 3 of the 'Configure CoralogixSSO for SSO section, and download the file named SAML XML Metadata.
Scroll up to the top of the SSO Configuration section and click Save.
Upload the metadata file to Coralogix web app via Settings, then Configure SAML.
Integrate with JumpCloud as a SAML IdP
Find instructions here.
Login with SAML
After SAML has been activated for your account you may access it using SSO.
Enter Coralogix.com, then Login and insert your team name.

In the next window, choose SSO login (for example, SIGN IN WITH GOOGLE) to log as a user.

If the username you used to log in was used with Coralogix in the past (for example, the administrator wanted to block the access and removed the username), then it will be required by the administrator to approve it. In that case a request was sent to your administrator, wait for his invitation email.

Join request received by the administrator:

Administrator panel after receiving join request from a user, click Approve to send an invitation to the user.
Invitation sent to you:

Now you can enter Coralogix with SAML SSO.
Finalize any additional configuration or verification needed on Coralogix’s side.
Keycloak is an open-source identity and access management solution offering single sign-on (SSO) capabilities. It allows users to authenticate across multiple applications using a single set of credentials. Integrating Keycloak with Coralogix via SAML enhances security, streamlines user authentication, and centralizes identity management. This integration enables users to securely access Coralogix with their existing Keycloak credentials, simplifying access control and enhancing the overall user experience.
Integrate Keycloak SSO with Coralogix using SAML
Follow the steps below to successfully set up the SAML integration between Keycloak and Coralogix.
Prerequisites
Configure the following entities and parameters.
-
Keycloak:
-
Operational Keycloak server
-
Realm ready for the integration
-
Users in the realm
-
-
Coralogix:
-
Coralogix team
-
Coralogix team URL
-
Coralogix team ID number (Settings, then Send Your Data)
-
Service Provider Metadata URL (Settings, then Configure SAML)
-
Assertion Consumer Service URL (Settings, then Configure SAML).
-
Client Certificate PEM, see details below
-
Keycloak configuration
In the Keycloak admin console, create a new realm or use an existing one for the integration.
Export SAML 2.0 identity provider metadata.
- In the Keycloak admin console, navigate to Configure, then Realm Settings.
- Click SAML 2.0 Identity Provider Metadata.
- Save the metadata as an XML file to be used for Coralogix configuration later.
Create a new client.
- Go to Clients, then Clients List, and click Create.
- Client type: SAML
- Client ID:
<your_CX_team_service_provider_metadata_URL> - Name: Coralogix (or any other meaningful name)
- Description (optional)
- Configure client settings.
- Root URL:
<your_CX_team_URL> - Home URL:
<your_CX_team_URL> - Valid redirect URIs:
<your_assertion_URL> - Valid post logout redirect URIs:
<your_CX_team_URL> - IdP-initiated SSO URL name: leave empty
- IDP Initiated SSO Relay State:
<your_team_ID_number><Your Team ID number> - Master SAML Processing URL:
<Your CX Team Service Provider Metadata URL>
- Root URL:
- Adjust SAML capabilities.
- After saving your changes, go to the Settings tab.
- Under SAML capabilities, change the Name ID format to email.
- Configure signature and encryption.
- In the Signature and Encryption section, enable Sign assertions.
- Replace the default certificate.
- Go to the Keys tab.
- Verify that the Client signature required option is enabled.
- Replace the existing certificate with the PEM certificate (public key) provided by Coralogix.
- Important: This certificate contains the public key for Coralogix, used in SAML integrations to verify the identity of Coralogix and ensure secure, authenticated communication.
-----BEGIN CERTIFICATE-----
MIIDUTCCAjmgAwIBAgIUTnz0Hc7WgtSevnVoflIIrEQGWIMwDQYJKoZIhvcNAQEL
BQAwODESMBAGA1UECgwJQ29yYWxvZ2l4MRAwDgYDVQQLDAdTU08gS2V5MRAwDgYD
VQQDDAdTU08gS2V5MB4XDTI1MDcwNzA4MTAwMVoXDTI2MDcwNzA4MTAwMVowODES
MBAGA1UECgwJQ29yYWxvZ2l4MRAwDgYDVQQLDAdTU08gS2V5MRAwDgYDVQQDDAdT
U08gS2V5MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAp5NEDeVE1fJp
m3MhoO9oDVXHgHio49EX7v3mljhQgLM+9JJwkUOotxrHDaOmCsn6wYJqWjZX/a29
NfavGR7+rDRb73V2GAJuBllE5E10BQG0rrBVfh+kHe1JV/9fXh2JrORhfpO30lXf
pY4H8OD3ViwCqxt1Icl7yiQn16h0IWgvi1mtULz4LafaZ3P0qxgGjwGEyX1qtHmj
HFfasvbagFnv/nKpcq3VnTrrgc/DloCg/qOGmIBHr2vzhEj2KO1WISu1ze7Umm1g
gM0xvoV5LHHYKygeui1qxRZ2rmPcvL3KYjFbJ9OYAmeTjS0YtvnwLYmQVk3LWsn+
p2Z7GlEByQIDAQABo1MwUTAdBgNVHQ4EFgQUw9ZCqsREOb50UFtmLBwo4CD6Fp8w
HwYDVR0jBBgwFoAUw9ZCqsREOb50UFtmLBwo4CD6Fp8wDwYDVR0TAQH/BAUwAwEB
/zANBgkqhkiG9w0BAQsFAAOCAQEAobBC38kPge59hDwONtILdV5LhnFXhV+rruBl
60rtD1Hr6x5HDLCROk7sCVd8t8fM0CSu0UAEs4mJZkUUmiOsEGMOAUlS/IqSUgdm
yyq6BSWK64sjsWlUae77u7LtfGbSZizhpqFDgUUi6jWnvkXKScuBb4TlhAsUBSD5
UtWSHLXokdT5TwO+Xh0JBetbzO7ozL/JE0D8O429mDVE2RK5KUj0VgPU/lzTJ8hU
DgHvyrwhJu6Ew/vrMs+FUHwiS4jw9G8ve1TlimmjQhDtbrkAO5d0FygF/CXEZuX0
irsxb1dTWS8oK0bmpDKdaXCShNukLkhiejntXhaLFBIa0TK3WQ==
-----END CERTIFICATE-----
- Configure roles.
- Go to Roles and create a new default role.
- Add the necessary users/groups to this role.
- Save the client configuration.
Coralogix configuration
In Coralogix platform, navigate to Settings, then Account, then Configure SAML and activate SAML.
Upload the Keycloak Identity Provider Metadata XML file that was exported earlier.
Finalize any additional configuration or verification needed on Coralogix’s side.