Parsing Rules
Parsing rules skip logs above the processing size limit
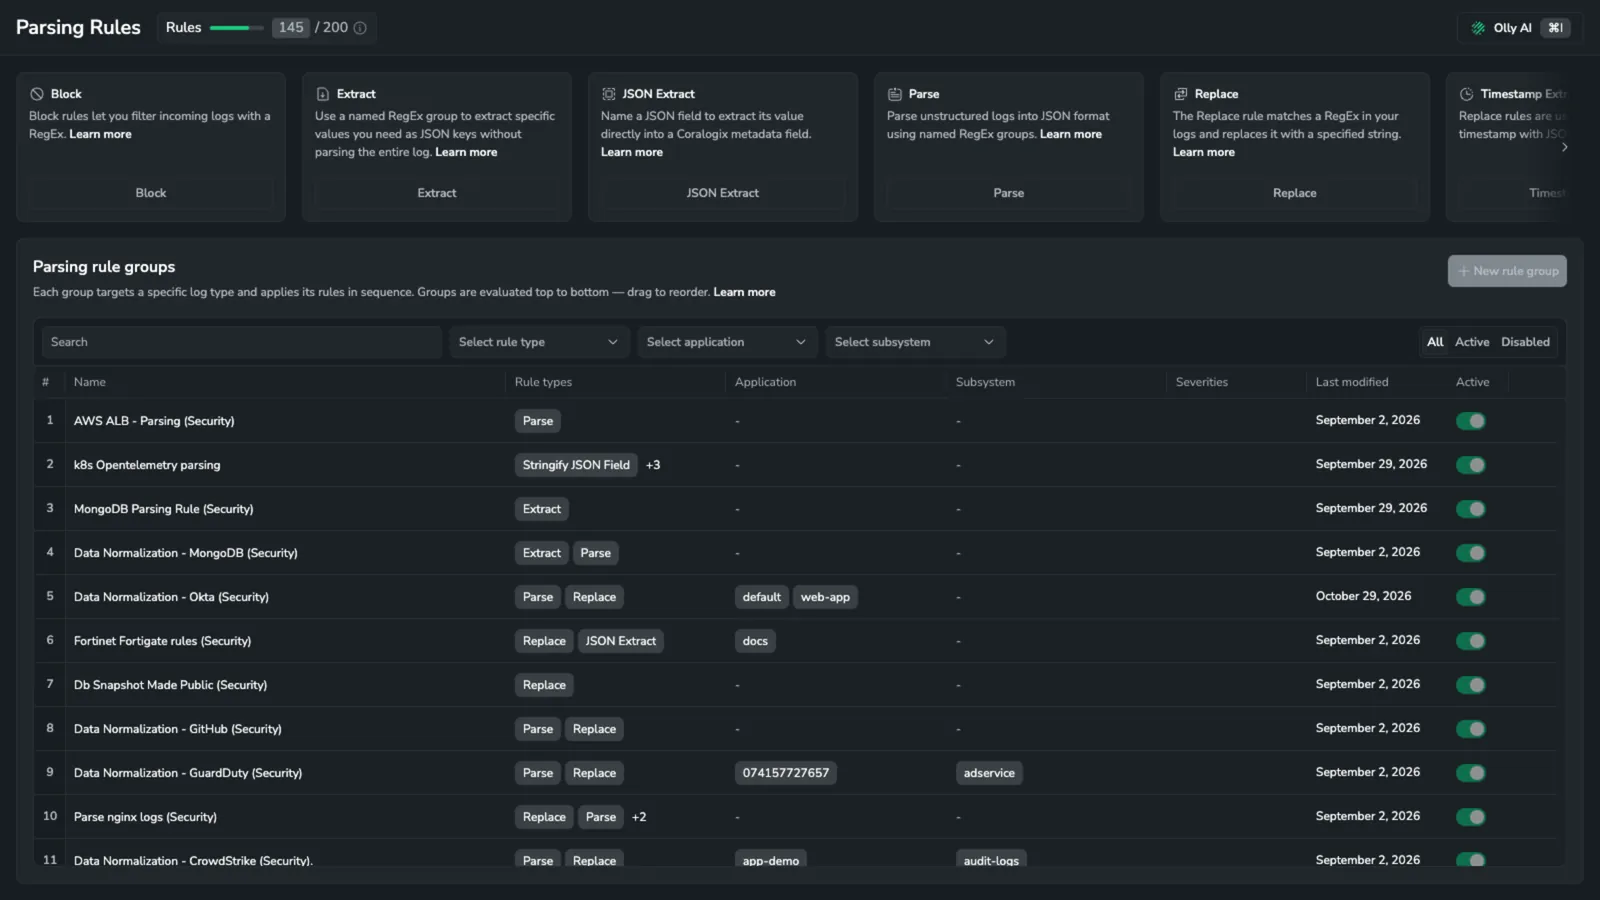
The docs now state that parsing rules are not applied to logs larger than the processing size limit. Block, Replace, and Remove Fields rules do not run on these logs, so sensitive data they contain is not blocked or masked. To protect sensitive data in large logs, filter it at the shipper level. Learn more
View as code (Beta)
Preview the Terraform and Kubernetes YAML representation of any saved rule group. Open from the rule list ⋮ more actions menu → View as Code. Tabs for Terraform (default) and K8s, with copy, download, search, and collapse/expand controls. Learn more
Custom log enrichment and log normalization
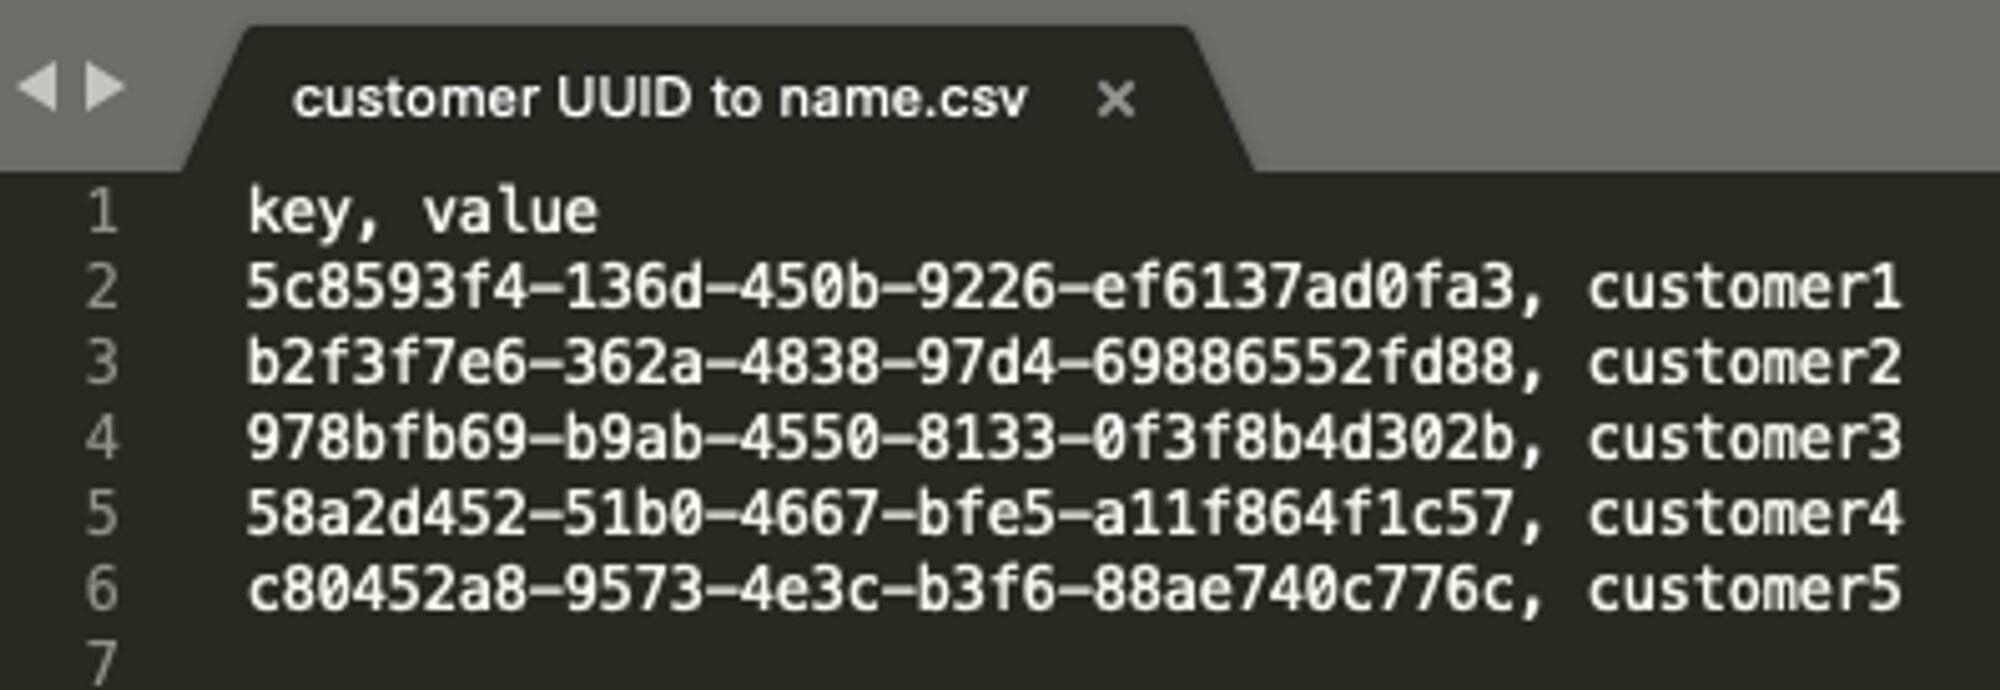
Custom log enrichment is now even more intuitive, enrich logs from specific columns in your CSV file, download enriched files, and use them as data sources in DataPrime queries. Learn more
Log normalization, standardize keys for commonly occurring values across various security log types. Learn more
Stringify and Parse JSON Field rules
New Parsing Rules. Stringify JSON Field and Parse JSON Field rules to parse escaped JSON values within a field to a valid JSON object and vice versa. Learn more