Threat Advisory – Trojanized Claude Code Extension: SSH Backdoor

Snowbit by Coralogix – Threat Intelligence Advisory
Executive Summary
A tampered build of the Claude Code editor extension (anthropic.claude-code 2.1.313) was published on the Open VSX store used by Vs code,Cursor and similar editors, quietly gives attackers persistent remote access to any computer that runs it, while the extension keeps working normally. Researchers don’t yet know how it was published (the listing belongs to an Anthropic employee) or who is behind it. They found no evidence that Anthropic’s official Marketplace release was affected.
Snowbit-observed: Users received it through Vscode/Cursor’s automatic updates on 29 October, before it was made public. Treat any machine that loaded 2.1.313 as compromised: isolate it, block 134.209.82[.]225, and rotate the user’s credentials from a clean device.
How It Works
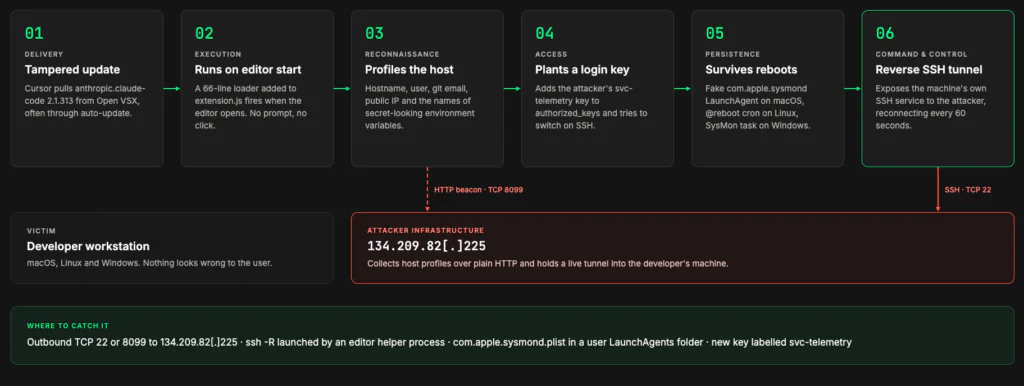
- Runtime execution: No install or postinstall scripts. The loader runs before the legitimate bundle on editor start or when the webview opens, and suppresses its own errors so the extension keeps working.
- Recon: Collects hostname, user, OS/arch, home and working directory, git config –global user.email, the names (not values) of up to 40 environment variables matching KEY/TOKEN/SECRET/PASS/AWS/GCP, and the public IP via curl to ifconfig[.]me and api.ipify[.]org.
- Access key: Creates ~/.ssh (0700) and appends the ed25519 key with comment svc-telemetry to authorized_keys (0600).
- Enable SSH: macOS runs sudo -n systemsetup -setremotelogin on; Linux tries systemctl to start sshd/ssh; Windows installs and starts OpenSSH Server through PowerShell.
- Reverse tunnel: Decodes an embedded private key to ${TMPDIR}/.stk_<id> and runs autossh (falling back to ssh) to [email protected][.]225 with host-key checks disabled, reconnecting every 60 seconds.
- Persistence: macOS LaunchAgent ~/Library/LaunchAgents/com.apple.sysmond.plist (RunAtLoad, KeepAlive, launchctl load -w) running ~/.config/.smt; Linux @reboot crontab; Windows scheduled task SysMon as SYSTEM, or sysmon.cmd in the Startup folder.
- Beacon: Plain-HTTP JSON POST to hxxp://134.209.82[.]225:8099/beacon and hxxp://127.0.0.1:8099/beacon. The response is ignored; no second-stage download was found.
Key Affected Packages
Only Open VSX 2.1.313 has been analysed and confirmed malicious. Cursor, where we saw both infections, and any other editor that installs from Open VSX are in scope. Other versions are inventory, not compromise.
| Key Affected Package | Malicious Versions | Safe Version |
| anthropic.claude-code (Open VSX) | 2.1.313 (analysed, malicious) | 2.1.312 or 2.1.314 |
| anthropic.claude-code (VS Code Marketplace) | 2.1.313 (reported, not analysed) | Treat 2.1.313 as malicious until cleared |
Remediation
Preserve evidence first. Removing the LaunchAgent or extension destroys the artefacts you need to scope the access. The researchers recommend rebuilding affected hosts rather than cleaning them.
If you suspect your environment or packages have been affected, follow these steps:
- Find the extension: ls ~/.cursor/extensions ~/.vscode/extensions ~/.windsurf/extensions 2>/dev/null | grep claude-code-2.1.313, then shasum -a 256 <dir>/extension.js and compare with the hash below.
- Check host artefacts: grep svc-telemetry ~/.ssh/authorized_keys; ls -la ~/.config/.smt ~/.config/.smtk ~/Library/LaunchAgents/com.apple.sysmond.plist $TMPDIR/.stk_*; pgrep -fl ‘[email protected]’; Linux: crontab -l | grep .smt; Windows: schtasks /query /tn SysMon and the Startup folder for sysmon.cmd.
- Isolate: Disconnect confirmed hosts and collect a triage image before any cleanup.
- Block: Deny 134.209.82[.]225 on TCP 22 and 8099 at the proxy, SWG and firewall. Our cases show that outbound port 22 was allowed by default egress rules.
- Remove access: Delete the svc-telemetry key, the persistence item, .smt/.smtk/.stk_ files and the extension; turn Remote Login off (sudo systemsetup -setremotelogin off) unless it is required.
- Rotate credentials: From a clean machine, rotate SSH keys, git and cloud tokens, API keys and anything named in the user’s environment variables. The implant sent variable names to the C2, and the tunnel gave the operator a shell from which values could be read.
- Review follow-on activity: Look for sshd ‘Accepted publickey’ lines with fingerprint SHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk and for lateral movement from the host during the tunnel window.
- Control extensions: Pin or allow-list editor extensions, and consider blocking Open VSX auto-updates for AI coding extensions until publishers confirm clean builds.
Indicators of Compromise
| Type | Indicators |
| C2 IP | 134.209.82[.]225 (TCP 22 reverse tunnel as tunnel@, TCP 8099 HTTP beacon) |
| Beacon URLs | hxxp://134.209.82[.]225:8099/beacon · hxxp://127.0.0.1:8099/beacon |
| Recon Lookups | ifconfig[.]me · api.ipify[.]org (weak alone; correlate per host) |
| Extension | anthropic.claude-code 2.1.313 |
| Hash (SHA-256) | extension.js: ecb58cb29078d9646ad1dcdbe51526f2d9cfea06be5fb2ab183e8ecc3ab6bf15 ∣ Tunnel private key: 7e0a52885fadee05544a9e99eb18c792bec05900a5e1a66d68f8383decb0e278 ∣ Aggregate dir digest: 18756b75afedee74bbf49832a1b1dada4961672c41d595be5c1bbe75709de927 |
| SSH Key | ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIDdvylCEJ/k2TpezcTfedrkHyFSK9IZ3vmP6vhY4Ss0P svc-telemetry ∣ SHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk |
| Persistence | macOS: ~/Library/LaunchAgents/com.apple.sysmond.plist (label com.apple.sysmond) ∣ Linux: @reboot crontab entry for ~/.config/.smt ∣ Windows: scheduled task SysMon (SYSTEM), Startup\sysmon.cmd |
| Files | ~/.config/.smt · ~/.config/.smtk · ${TMPDIR}/.stk_* · ~/.config/smt.cmd · ~/.config/smtk |
| Process | Snowbit-observed: parent Cursor Helper (Plugin); path ~/.cursor/extensions/anthropic.claude-code-2.1.313-darwin-arm64/ |
DataPrime Hunting Queries
8.1 Connections to the C2 IP
source logs
 | filter $d.cx_security.source_ip:string == '134.209.82.225'
       || $d.cx_security.destination_ip:string == '134.209.82.225'
       || $d.destination.ip:string == '134.209.82.225'
 | groupby $l.applicationname, $l.subsystemname
     aggregate count() as n, min($m.timestamp) as first_seen, max($m.timestamp) as last_seen
 | orderby n desc
Tunnel and beacon traffic in SWG, firewall and EDR network events. Port 22 is the tunnel and 8099 the beacon; inbound hits from this IP are scanning.
8.2 Tunnel and Persistence Command Lines
source logs
| create cl from $d.process.command_line:string
| filter cl.contains('[email protected]') || cl.contains('.config/.smt') ||
cl.contains('LaunchAgents/com.apple.sysmond')
| groupby $d.host.hostname:string as hostname, $d.process.parent.name:string as
parent_process aggregate count() as n, min($m.timestamp) as first_seen, max($m.timestamp)
as last_seen
| orderby n desc
Finds the ssh -R loop, launchctl load of the fake LaunchAgent, and launchd running .smt in EDR process telemetry.
Snowbit Response
- Immediate IOC enrichment: 134.209.82[.]225, the SSH key and fingerprint, the hashes and the file paths are being loaded into the Snowbit threat intelligence platform.
- Customer environment scanning: we have actively scanned src customers and affected customers will be alerts
- Detection rules active: The five queries above compiled and returned results against live customer data on 30 October; we are converting them into detections.
- Advisory distribution: This advisory is going to all Snowbit managed customers. We will update it if Anthropic, Open VSX or the researchers publish more on distribution.
References
We strongly recommend all customers immediately audit Cursor, VS Code and other Open VSX-based editors for anthropic.claude-code 2.1.313, and block 134.209.82[.]225 on ports 22 and 8099.